
DAILY BRIEFING
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
Today's briefing covers an actively exploited Orkes Conductor RCE, a SolarWinds ARM hard-coded key flaw, and AI-assisted research revealing chained account takeover flaws at OpenAI.
5 stories2 min read
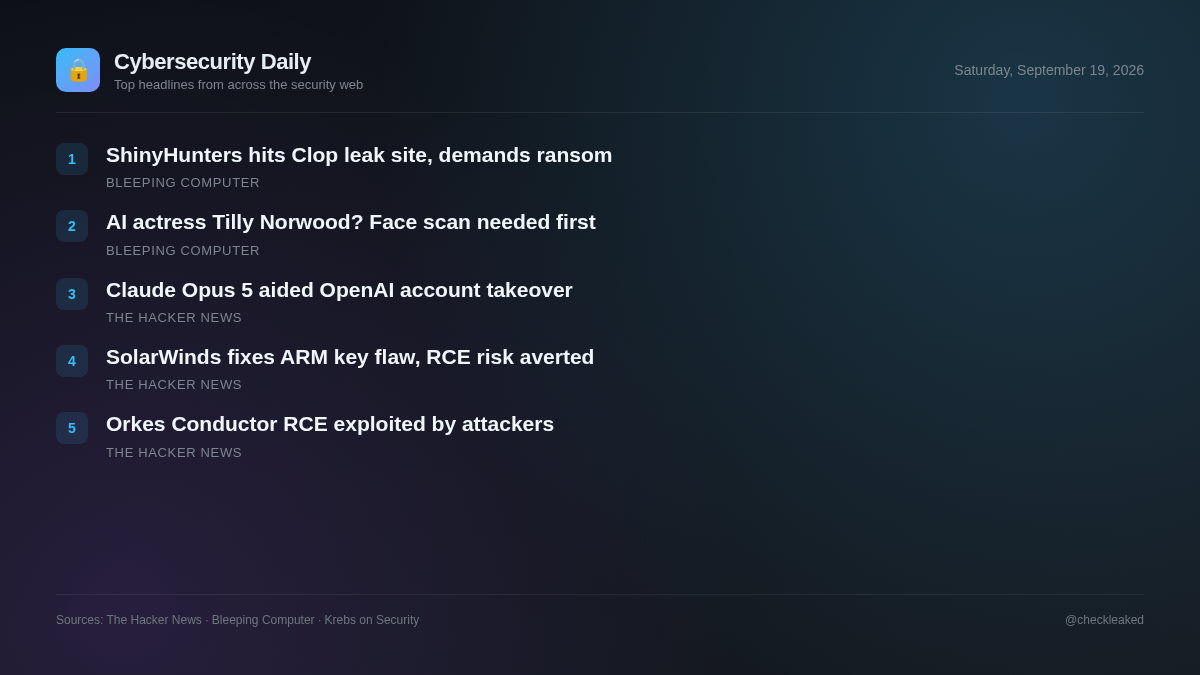
In parallel, security research highlights the growing role of AI models in finding security vulnerabilities. Researchers using Claude Opus 5 chained bugs in an open-source forum and internal authentication systems to access internal OpenAI code repositories.
Organizations using Orkes Conductor or SolarWinds ARM should prioritize upgrading vulnerable systems immediately, while development teams must ensure proper input sanitation and authentication checks across all user-facing services.
Critical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the Wild
A critical pre-authentication remote code execution flaw (CVE-2026-58138) in Orkes Conductor 3.21.21 prior to 3.30.2 is being actively exploited in the wild. Attackers submit malicious inline workflow definitions containing JavaScript or Python expressions to bypass unsandboxed GraalVM evaluators.
- Why it matters
- Unauthenticated remote attackers can execute arbitrary OS commands via Java reflection or subprocess calls on exposed Orkes Conductor servers.
- What to do
- Update Orkes Conductor instances to version 3.30.2 or higher immediately.
Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws
Security researchers at Hacktron used Anthropic's Claude Opus 5 to chain a flaw in OpenAI's public Discourse help forum with a weakness in OpenAI's login system. The research demonstrated account takeovers of ChatGPT and Codex accounts for OpenAI employees and reached an internal OpenAI code repository within 72 hours.
SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE
SolarWinds patched an unauthenticated remote code execution vulnerability (CVE-2026-28326) in Access Rights Manager (ARM) versions 2026.2 and prior. The flaw carries a CVSS score of 8.8 and is caused by a hard-coded static key.
- Why it matters
- Unauthenticated remote attackers can leverage the hard-coded key to execute arbitrary code on servers running vulnerable instances of SolarWinds ARM.
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
No detailed news text was available due to a Cloudflare bot verification page blocking the source content.
Calling viral AI actress Tilly Norwood? Agree to a face scan first
No detailed news text was available due to a Cloudflare bot verification page blocking the source content.
Key takeaways
- Orkes Conductor versions 3.21.21 before 3.30.2 face active exploitation via unauthenticated RCE flaw CVE-2026-58138.
- SolarWinds patched CVE-2026-28326, an 8.8 CVSS hard-coded key flaw in Access Rights Manager 2026.2 and prior.
- Hacktron researchers used Claude Opus 5 to chain Discourse and login flaws, taking over OpenAI staff accounts.