
DAILY BRIEFING
Webinar: Which Google Workspace security controls actually matter?
Today's briefing covers a CVSS 10.0 Azure AI Foundry flaw, hijacked CDN domains, and Plugin4Shell vulnerabilities in AI coding agents.
5 stories2 min read
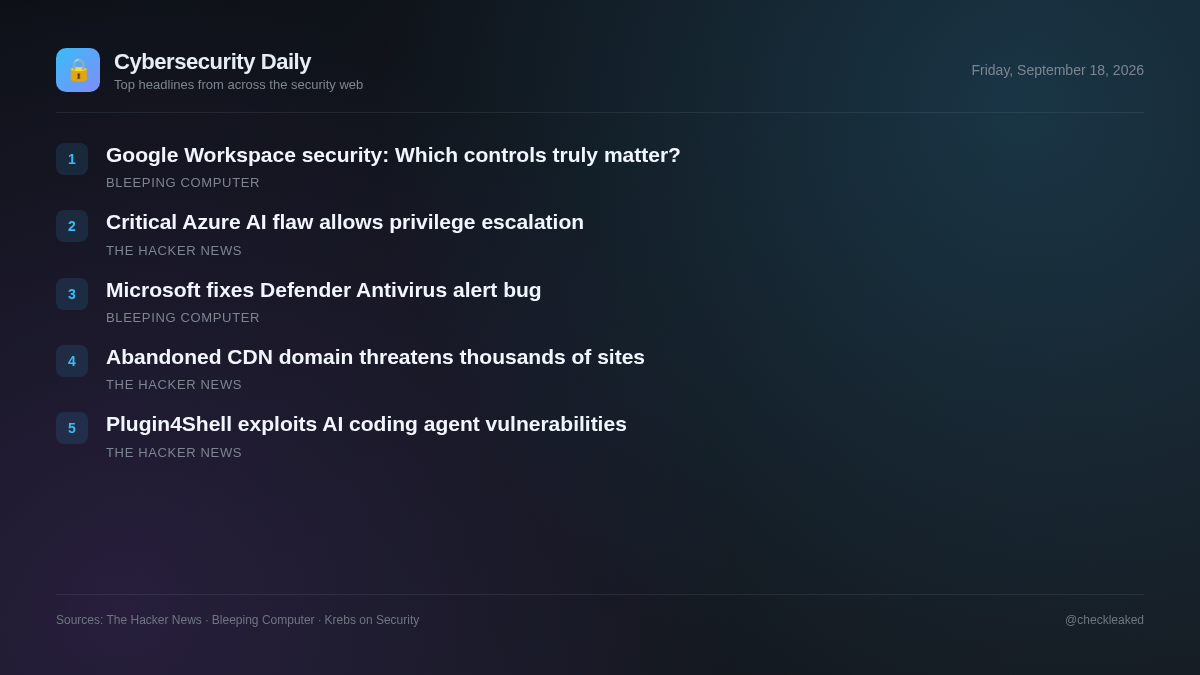
Today's threat landscape highlights critical risks in cloud infrastructure, third-party software supply chains, and AI development environments. Microsoft has addressed a maximum-severity privilege escalation vulnerability in Azure AI Foundry that required missing authentication checks, requiring no action from customers.
Security teams and developers should prioritize reviewing external scripts embedded in their web applications and update vulnerable AI development tools immediately.
Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege Escalation
Microsoft patched a maximum-severity privilege escalation flaw, tracked as CVE-2026-85889 with a CVSS score of 10.0, in Azure AI Foundry. Missing authentication for a critical function allowed unauthorized network attackers to elevate privileges. Microsoft applied fixes with no customer action required.
- Why it matters
- Enterprise organizations using Azure AI Foundry faced potential network-based privilege escalation due to missing authentication.
- What to do
- Confirm Azure AI Foundry cloud environment updates via Microsoft.
An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.
An abandoned CDN domain was re-registered in July 2025 by an owner holding wildcard DNS. Thousands of websites, repositories, and documentation pages retain hard-coded references to subdomains, allowing the owner to control served content without breaking caller functionality.
- Why it matters
- Websites calling legacy CDN domains risk executing arbitrary external scripts if abandoned infrastructure is repurposed.
Plugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding Agents
Air Security disclosed Plugin4Shell, a flaw in four AI coding agents where repository owners can swap pinned plugin code. Agents fetch code without validating it against the locked commit hash, enabling malicious substitutions via branch names. Patches were released for Claude Code and Codex.
- What to do
- Update Claude Code to version 2.1.179 and Codex to version 0.146.0.
Webinar: Which Google Workspace security controls actually matter?
Fast-growing companies face countless recommendations for securing Google Workspace, but not every control provides the same value.
Microsoft fixes bug behind ‘Defender Antivirus is turned off’ alerts
Microsoft has resolved a known issue that causes incorrect alerts warning that Defender Antivirus was turned off after installing recent updates.
Key takeaways
- Microsoft patched CVE-2026-85889, a CVSS 10.0 missing authentication flaw in Azure AI Foundry enabling privilege escalation.
- An abandoned CDN domain re-registered by a third party is still actively called by thousands of sites, presenting supply chain risks.
- Plugin4Shell vulnerabilities let attackers swap pinned plugin code across four AI coding agents by spoofing commit hashes.
- Anthropic patched Claude Code 2.1.179 and OpenAI patched Codex 0.146.0 against Plugin4Shell, while GitHub Copilot remains unpatched.