
DAILY BRIEFING
Uranium crypto exchange hacker convicted for stealing $53 million
Today's security roundup details the multi-stage Wazza phishing kit alongside major legal sentences for cybercriminals.
5 stories2 min read
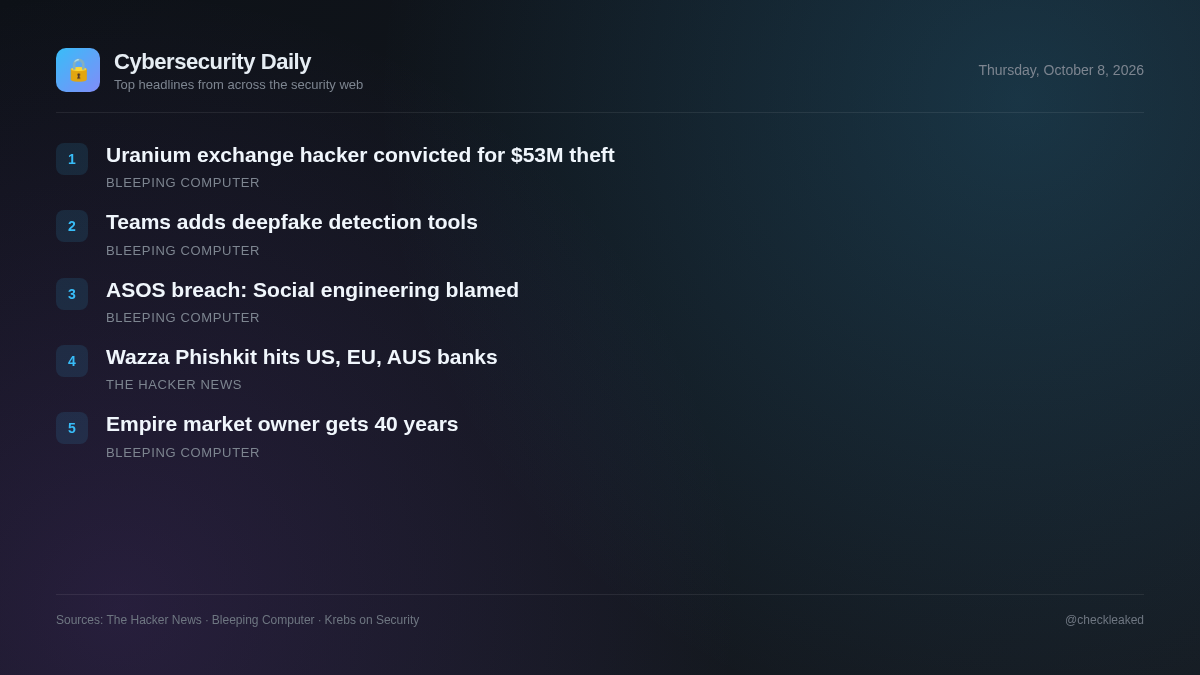
At the same time, law enforcement actions continue to deliver significant judicial outcomes against high-profile cybercrime operations, including major convictions and lengthy prison sentences related to illicit marketplaces and cryptocurrency thefts.
Wazza Phishkit Targets Banking, Government, and Manufacturing Across the US, EU, and Australia
ANY.RUN identified a new phishing kit named Wazza targeting banking, manufacturing, and government organizations across the US, Europe, and Australia. The threat uses a multi-stage routing chain to filter automated traffic and visitors before serving an Adobe-themed Device Code phishing lure.
- Why it matters
- Wazza hides the final lure behind multi-stage traffic filtering, frustrating automated detection tools and making initial link analysis less effective for security analysts and MSSPs.
Uranium crypto exchange hacker convicted for stealing $53 million
A Maryland man was found guilty of stealing more than $53 million after hacking the decentralized crypto exchange Uranium Finance twice in April 2021.
Microsoft Teams to get support for third-party deepfake detection tools
Microsoft will soon introduce support for third-party deepfake detection solutions and impersonation protection in Teams meetings.
ASOS links data breach to social engineering attack, credential theft
ASOS is sending updates to affected customers about the cybersecurity incident it suffered earlier this week, confirming that hackers accessed some personal data.
Owner of Empire cybercrime market gets 40 years in prison
The content of this story could not be processed as the source web page returned a Cloudflare bot verification challenge.
Key takeaways
- ANY.RUN identified Wazza, a phishkit using Adobe-themed Device Code prompts to target government, banking, and manufacturing sectors.
- Wazza employs a multi-stage routing chain and traffic screening to evade automated detection systems across the US, EU, and Australia.
- Law enforcement continues to achieve significant sentencing against individuals tied to large-scale cybercrime and market operations.