
DAILY BRIEFING
Webinar: How to Govern AI Agents, Reduce Excessive Access, and Control Shadow AI
Today's briefing highlights automated cloud exploitation, including a botnet abusing unauthenticated Docker daemons and destructive attacks against Azure service principals.
5 stories2 min read
Cloud security and identity administration teams must act immediately to enforce strict authentication, audit automated access rights, and lock down management APIs across environments.
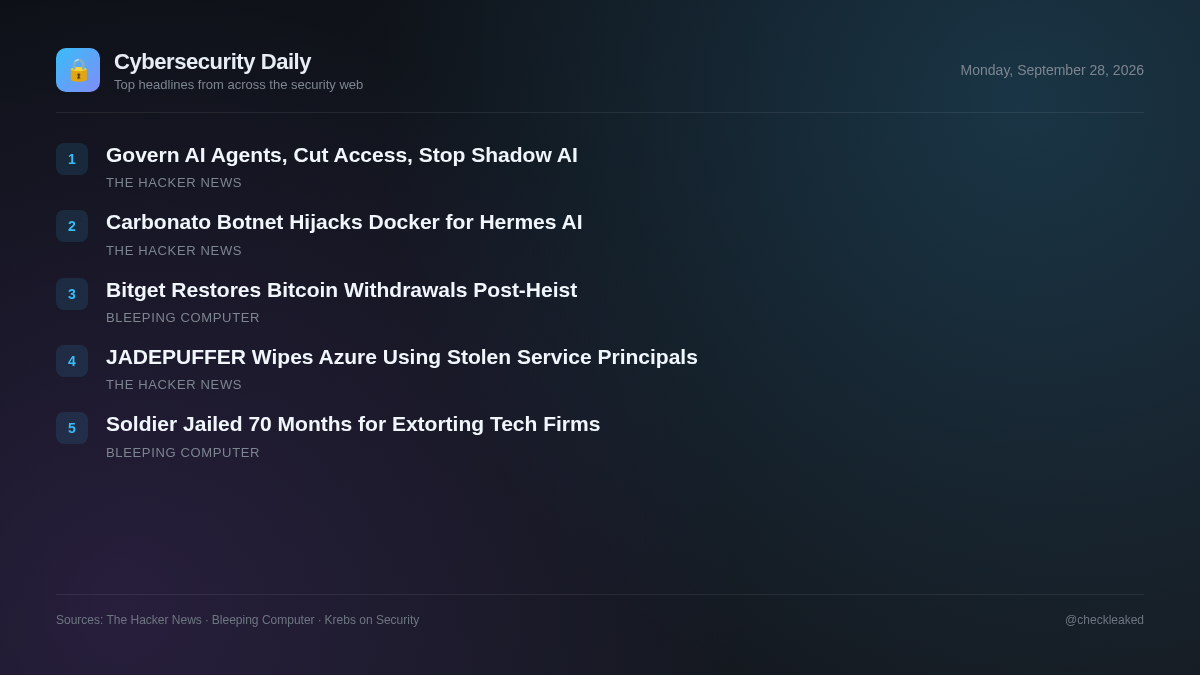
Carbonato Botnet Compromises Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent
The Carbonato botnet is compromising Docker daemons exposed without authentication on port 2375 to deploy the open-source Hermes AI Agent, configuring its persona file to execute attacker commands received via Telegram.
- Why it matters
- Exposed Docker hosts face automated compromise, host takeover, credential theft, and worm-like lateral movement across internal networks.
JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources
Threat actor JADEPUFFER, tracked by Microsoft as Storm-3168, used compromised service principals to carry out destructive resource deletion across an Azure environment over an 18-hour window in June 2026.
- Why it matters
- Compromised service principals with elevated rights enable threat actors to wipe Azure Storage Accounts, Key Vaults, SQL databases, and virtual machines.
Webinar: How to Govern AI Agents, Reduce Excessive Access, and Control Shadow AI
Okta research highlights growing security gaps in enterprise AI agent deployment, showing that many organizations lack purpose-built identity governance frameworks and rely on legacy service accounts or shared credentials to manage non-human agent access.
- Why it matters
- Organizations deploying AI agents without specialized identity governance controls risk excessive, unreviewed access to corporate APIs, sensitive datasets, and business applications.
Bitget resumes Bitcoin withdrawals after $387.5 million crypto heist
Cryptocurrency exchange Bitget has resumed Bitcoin withdrawals suspended after suspected North Korean hackers breached its systems last week and stole over $350 million.
- Why it matters
- Details regarding the impact on accounts and systems could not be retrieved directly from the provided source page.
US soldier gets 70 months in prison for extorting 10 tech, telecom firms
A news article detailing a US soldier receiving a 70-month prison sentence for extorting 10 technology and telecommunications firms was blocked by a Cloudflare anti-bot check in the provided source.
- What to do
- Review official legal announcements and court filings directly for information regarding the case.
Key takeaways
- Carbonato botnet targets Docker daemons exposed without authentication on port 2375 to deploy the Telegram-controlled Hermes AI agent.
- Storm-3168 compromised service principals in Azure to delete Key Vaults, SQL databases, and virtual machines during an 18-hour attack.
- Survey data shows 21 percent of organizations still rely on shared credentials or broad-permission service accounts to manage AI agents.