
DAILY BRIEFING
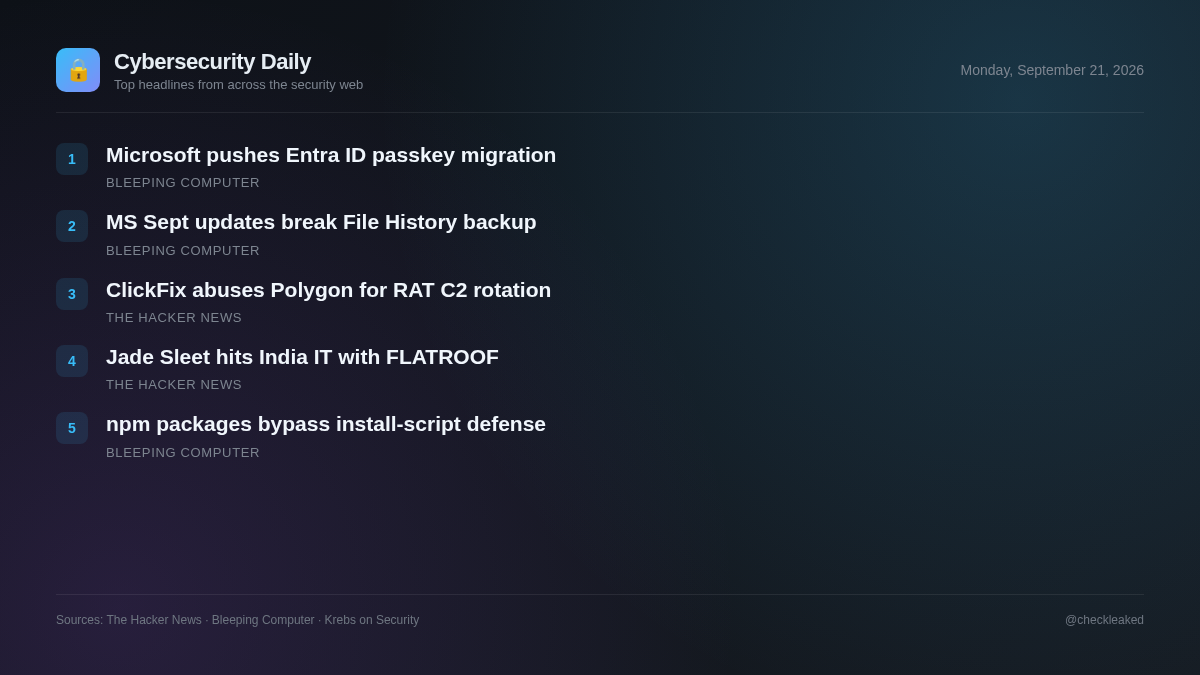
Microsoft reminds admins to migrate Entra ID users to passkeys
Today's briefing covers new ChainScript RAT deployments leveraging Polygon smart contracts and Jade Sleet's macOS backdoor attacks against IT providers.
5 stories2 min read
Threat actors are increasingly combining social engineering tactics with novel infrastructure resilience techniques. Recent campaigns highlight how adversaries bypass traditional detection by leveraging decentralized networks and targeting developer supply chains.
ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure
Threat actors are using ClickFix lures disguised as Spotify, Zoom Workplace, and Microsoft Teams to deploy the ChainScript RAT. ChainScript employs Polygon smart contracts via EtherHiding for C2 discovery and offers CMD, PowerShell execution, screenshot capture, and crypto wallet theft capabilities.
- Why it matters
- Users lured into running fake software installers face full system compromise, remote execution, and cryptocurrency wallet theft.
Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors
North Korean threat actor Jade Sleet compromised an India-based IT services provider, targeting developers using FLATROOF and ROOFDECK macOS backdoors. Both backdoors were previously deployed in the KelpDAO LayerZero bridge exploit.
- Why it matters
- IT service providers and developers are targeted for initial access, exposing downstream target networks to persistent macOS backdoors.
Microsoft reminds admins to migrate Entra ID users to passkeys
Microsoft has reminded admins to migrate Entra ID users to phishing-resistant authentication methods to avoid sign-in disruptions after it retires SMS first-factor sign-in starting in February 2027.
Microsoft: September updates break File History backup feature
Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after installing the September 2026 security updates.
Malicious npm packages evade install-script defenses at runtime
The context for the story on malicious npm packages evading install-script defenses at runtime consists solely of a Cloudflare security verification page.
Key takeaways
- ChainScript RAT uses ClickFix lures disguised as Teams, Zoom, or Spotify to compromise endpoints.
- ChainScript uses Polygon smart contracts in an EtherHiding technique to dynamically resolve WebSocket C2 servers.
- North Korean group Jade Sleet compromised an Indian IT provider using FLATROOF and ROOFDECK macOS backdoors.
- Jade Sleet continues to target software developers and IT services companies to infiltrate downstream networks.